Nmap (+ Zenmap)
Network and port scanner for host discovery and perimeter audit.
Open source Desktop download
- Platforms
- Windows/macOS/Linux/BSD
- Licence
- Open source — NPSL
- Price
- Free
- Category
- Network & diagnostics
- Updated
- 2026-11-05
What it is
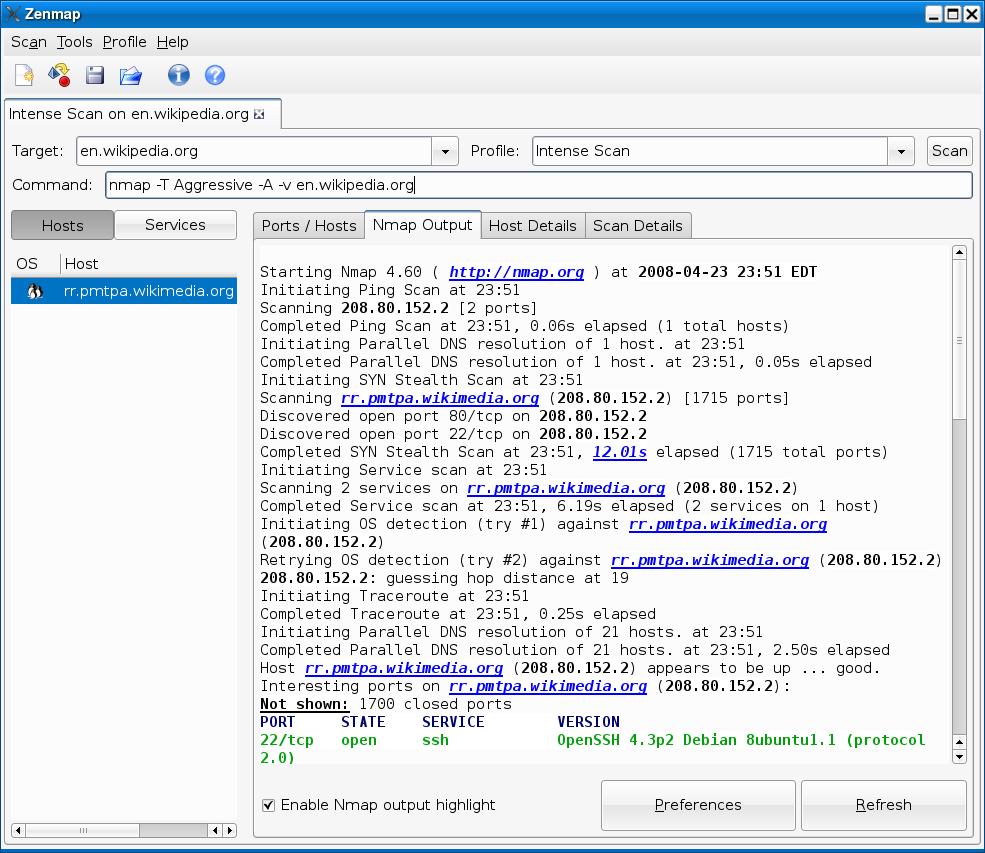
Nmap is a network and port scanner for discovering hosts, ports and services; Zenmap is its graphical front end. Administrators use it for device inventory, perimeter audits and checking which services are exposed.
Problems it removes
- You need to know which hosts and services are actually live on a subnet.
- An audit requires finding exposed or unexpected open ports on the perimeter.
- There is no CMDB and you need to inventory what is really on the network.
How administrators use it
- Run a host-discovery sweep to map which hosts are up.
- Scan ports with service and version detection to see what is listening.
- Use Zenmap or save output files for repeatable, comparable audits.
Strengths & trade-offs
Strengths
- Deep, scriptable scanning via the Nmap Scripting Engine.
- Cross-platform and free.
- Service and OS fingerprinting.
Trade-offs
- Aggressive scans can trigger IDS alerts — scan only what you are authorised to.
- The command-line power has a learning curve.
Common questions
Is scanning with Nmap legal?
On your own or explicitly authorised networks, yes. Scanning systems you do not control can be unlawful.
What is Zenmap?
The official graphical front end for Nmap, useful for building and visualising scans.